Compliance for MedTech – where regulation meets product success
Proliance is the specialist compliance partner for medical technology facilities. We cover all regulatory requirements – GDPR, NIS2, ISO 27001, and AI governance – with over 300 healthcare facilities under our care, more than 50 certified experts, and a platform that truly works in everyday practice.




Compliance for MedTech: GDPR, MDR, NIS2, and the EU AI Act from a single source
MedTech companies – including medical device manufacturers, medical software providers, and digital health startups – face one of the most complex regulatory environments in existence. GDPR, the EU Medical Device Regulation (MDR/IVDR), ISO 13485, NIS2, and the EU AI Act all overlap and must be complied with simultaneously. Proliance supports MedTech companies across the DACH region in implementing data protection, information security, and AI governance in a structured, legally compliant manner without unnecessary overhead.
Which type of MedTech company are you?
The compliance requirements for a medical device manufacturer differ fundamentally from those of a digital health startup or a software provider in a clinical setting. Proliance understands these profiles – and has a proven solution for each one.



Why MedTech compliance is about more than just GDPR
MedTech companies operate at the intersection of medicine, technology, and regulation. Multiple sets of rules apply simultaneously, often influencing one another. What counts as full compliance in other industries is often just the starting point in the MedTech sector.


The Proliance service portfolio for MedTech
Proliance bundles all regulatory requirements for the MedTech industry into one offering: data protection, information security, and AI governance – with certified experts and a platform built for the complexity of this sector.
External data protection officer with MedTech expertise
Our DEKRA- and TÜV-certified data protection officers are familiar with the specific requirements in the MedTech sector – from the processing of clinical data to the GDPR-compliant design of medical devices. Your personal point of contact.

GDPR compliance for medical devices & medical software
Records of processing activities (ROPA), data processing agreements (DPA), data protection impact assessments (DPIA), and product-related privacy policies: we create and maintain all required documentation – legally secure and MDR-compliant.

MDR / IVDR: Data protection as a component of regulatory approval
The EU Medical Device Regulation sets its own requirements for data protection – from clinical evaluation to post-market surveillance. Proliance integrates the data protection aspects of your MDR and IVDR compliance directly into your technical documentation.

ISO 13485 & ISO 27001: From gap analysis to certification
Proliance guides you through the entire certification process – structured, on time, and with a clear focus on what is truly necessary. No overheads, no unnecessary bureaucracy.

Information Security & NIS2 for MedTech
Cyberattacks on MedTech companies are on the rise – and NIS2 makes information security mandatory for everyone supplying critical infrastructure. Proliance analyses your exposure, develops a bespoke ISMS and implements it with you.

AI Governance & EU AI Act
Are you using AI in your products or internal processes? Proliance classifies your AI applications according to the EU AI Act, assesses the risk potential and develops a practical AI governance framework – so you can use AI in a legally compliant and future-proof way.

Proliance 360 – Compliance platform for the MedTech industry
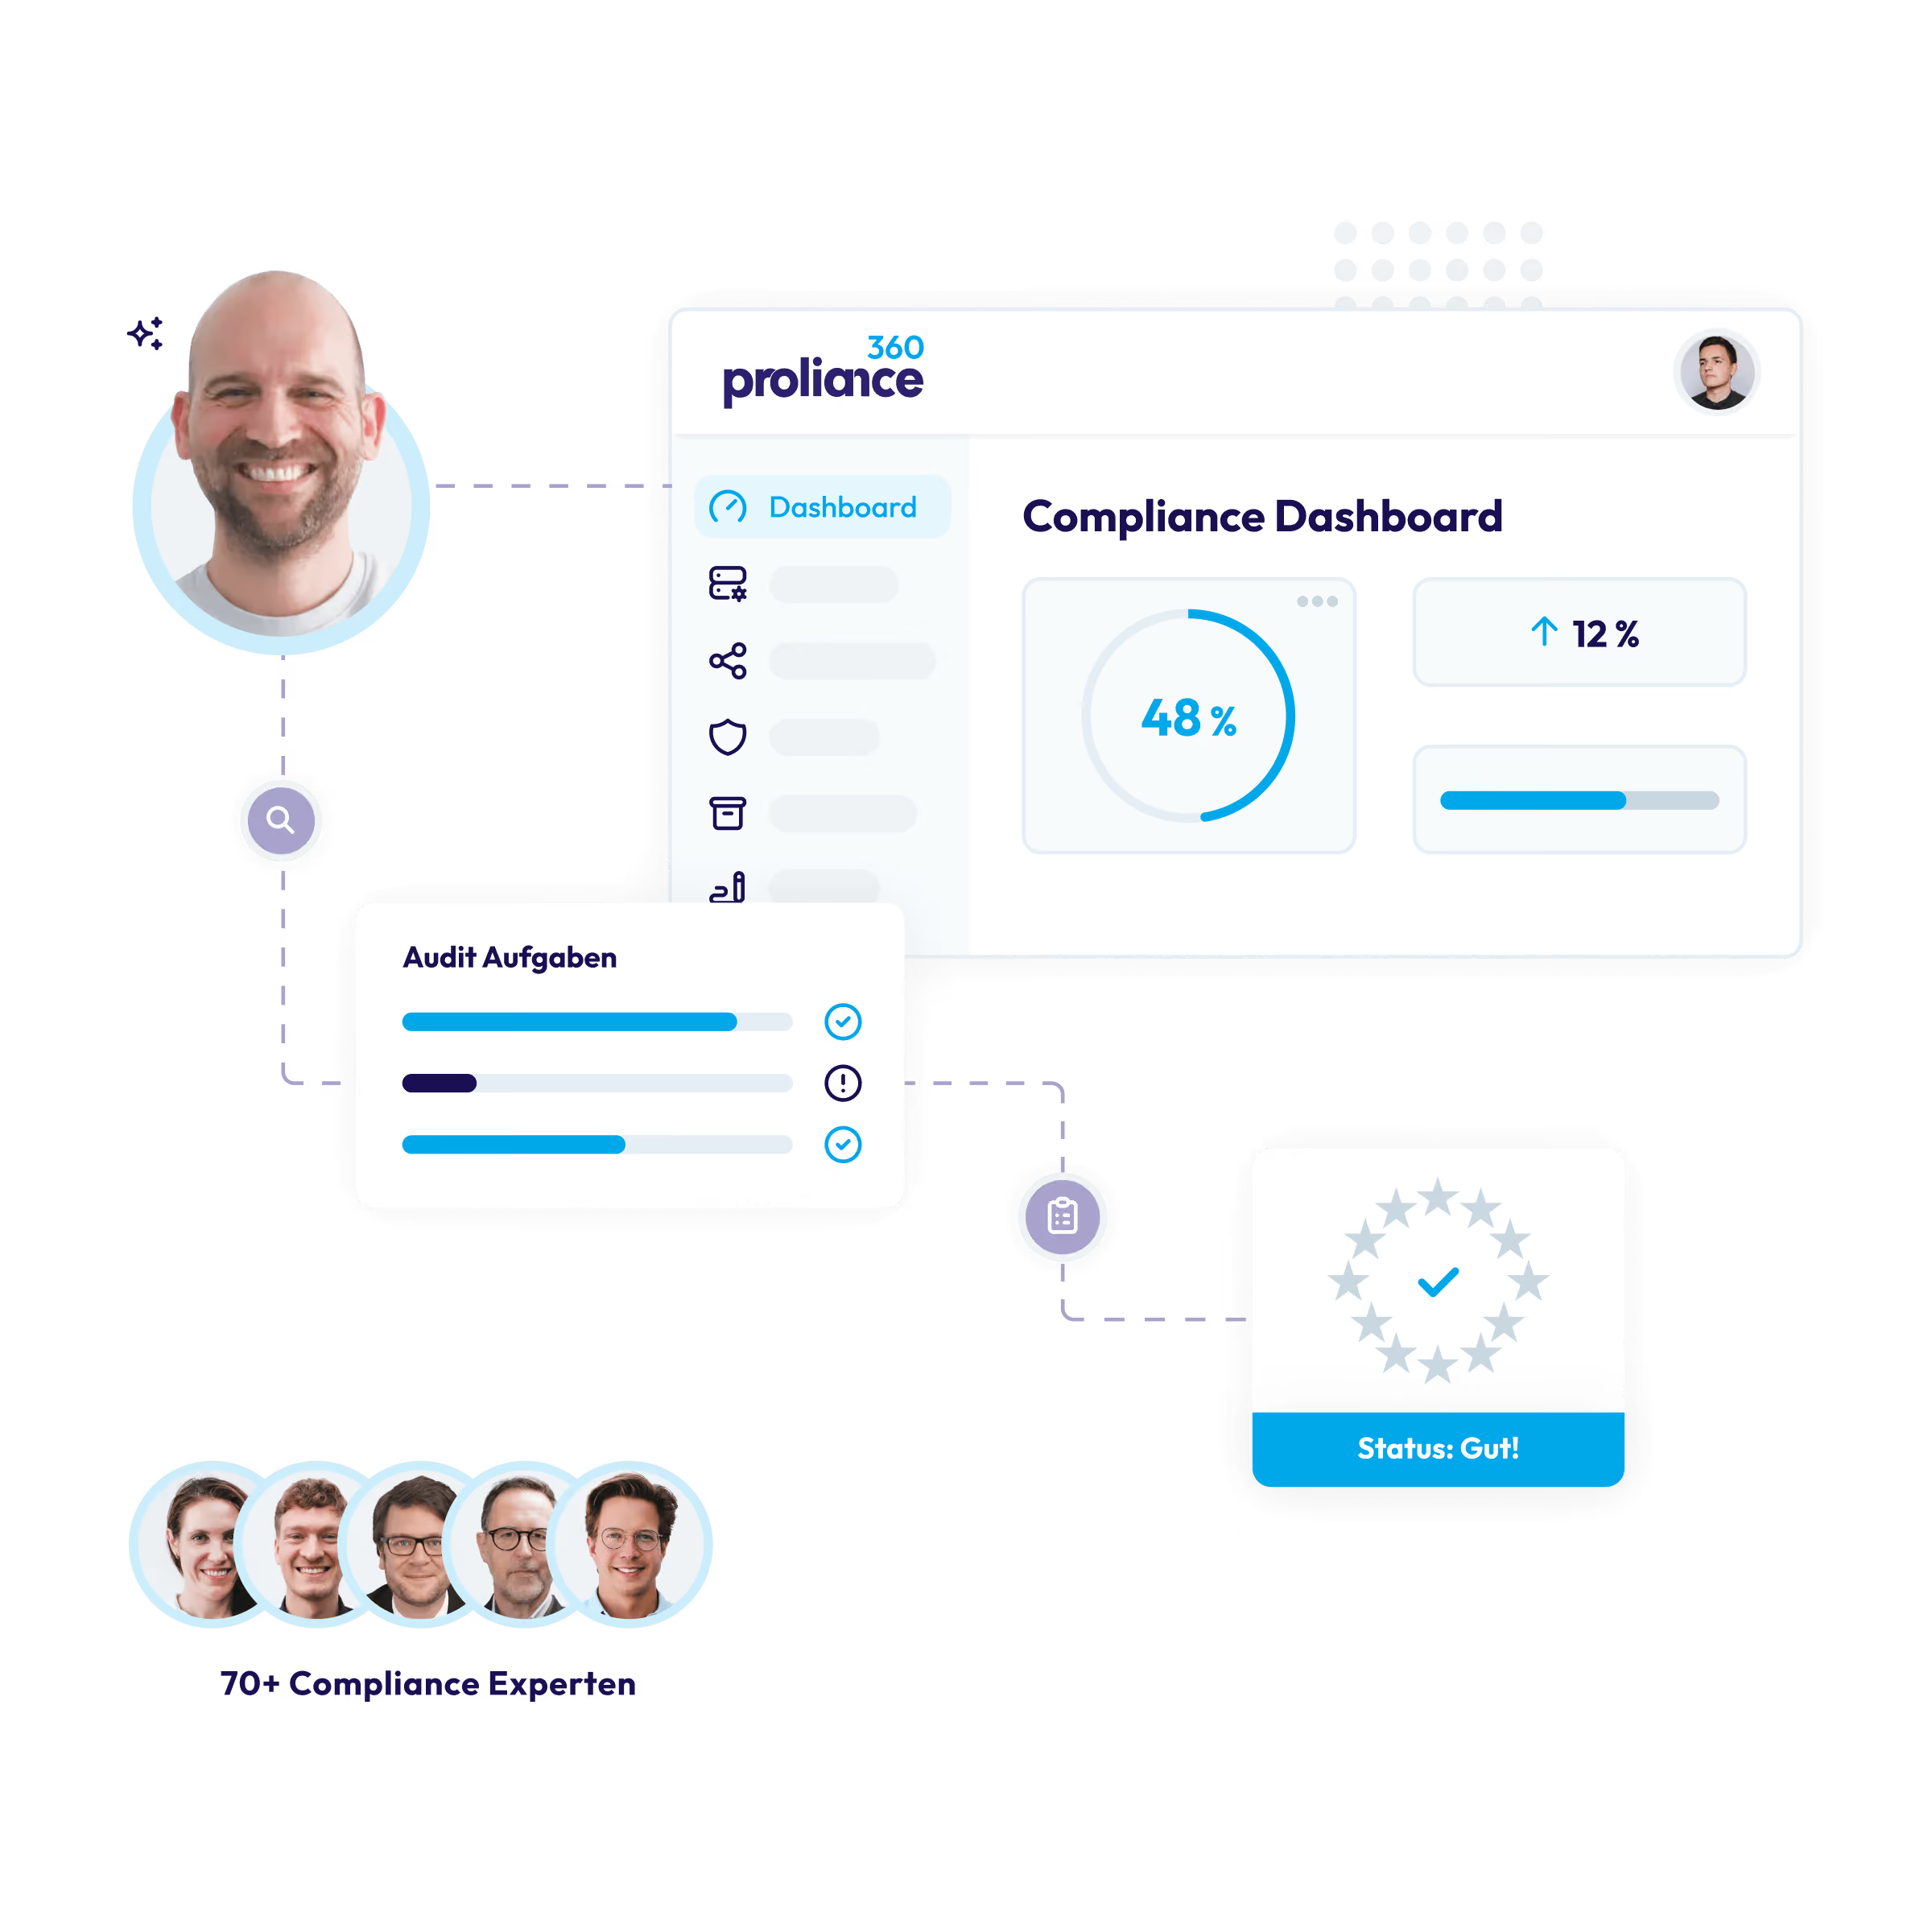
All tasks, documents, deadlines and evidence for data protection, information security and AI governance in one place. Developed by compliance experts for compliance experts. Hosted in Europe, audit-ready, and intuitive to use.
Over 3,000 companies work with Proliance – including MedTech manufacturers and medical software providers


Compliance that matters to you and works in practice
We create bespoke service packages tailored to your company size, processes, and goals. Together, we implement data protection, information security, whistleblower protection, and AI governance in a way that is legally compliant, clear, and practical for your day-to-day operations.



Frequently asked questions about data protection audits
Yes – in most cases. MedTech companies regularly process health data under Article 9 of the GDPR, which generally makes the appointment of a Data Protection Officer mandatory. This requirement also applies if 20 or more people are permanently involved in automated data processing. An external DPO with MedTech expertise is often the most efficient solution – Proliance takes on this role for MedTech companies throughout the DACH region.
The EU Medical Device Regulation sets out specific requirements for handling clinical data, post-market surveillance, and technical documentation – areas that overlap with the GDPR and ISO 27001. Manufacturers must ensure that patient data is processed in compliance with the GDPR and protected by appropriate security measures. Proliance integrates all three areas of requirement into a coherent compliance strategy.
ISO 13485 governs the quality management system for medical device manufacturers, yet it does not contain its own data protection requirements. However, many processes—such as traceability, customer complaints, and clinical evaluation—involve personal data and must be designed to be GDPR-compliant. ISO 27001 complements the system by addressing information security. Proliance aligns all three requirements and integrates them into a single, unified system.
SaMD is software that independently fulfils medical purposes, such as diagnosis, monitoring, or therapy support. It is subject to the EU MDR, must be developed in accordance with IEC 62304, and processes highly sensitive patient data. GDPR compliance, Data Protection Impact Assessments (DPIA), information security under ISO 27001, and, where applicable, AI governance under the EU AI Act are not optional extras, but prerequisites for approval. Proliance supports SaMD manufacturers throughout the entire compliance development process.
This depends on your role in the supply chain. MedTech companies that are classified directly as critical infrastructure, or that supply critical infrastructure, may fall under the scope of NIS2. The directive mandates enhanced security measures, incident reporting obligations, and regular compliance documentation. Proliance will analyse your specific NIS2 requirements and support you every step of the way, from the initial gap analysis to ISO 27001 certification.
AI-powered medical devices – such as those used for diagnostic imaging, clinical decision support, or automated risk classification – are frequently classified as high-risk AI under the EU AI Act. This entails risk assessments, transparency obligations, human oversight, and comprehensive documentation. Proliance helps you classify your AI applications, establish an AI governance framework, and integrate the requirements of the AI Act into your existing MDR processes.
Knowledge on data protection, information security, and AI compliance: guides, templates & magazine
Magazine


Guides & Reports
Data Protection Templates
Compliance in your facility – simple, secure, and from a single source.