
External Data Protection Officer
- Zertifizierte Datenschutzexpertise
- Persönlich an Ihrer Seite
- DSGVO-Compliance ohne Mehraufwand


Externer Datenschutzbeauftragter:
- Zertifizierte Datenschutzexperten an Ihrer Seite
- Antwort in 24 bis 72 Stunden, je nach Paket
- Transparente Preise ohne versteckte Kosten



What is an external Data Protection Officer?
Warum ein externer Datenschutzbeauftragter?
An external Data Protection Officer (DPO) is an independent expert whom a company contractually designates as the person responsible for operational data protection. Unlike an internal DPO, they are not an employee – they bring specialized expertise, independence, up-to-date legal knowledge, and experience, without being permanently on the payroll.
The legal basis is Articles 37–39 GDPR and Section 38 BDSG: Companies that exceed certain thresholds or process particularly sensitive data are obliged to appoint a DPO.
Ein externer Datenschutzbeauftragter (DSB) ist ein unabhängiger Experte, den Sie per Dienstleistungsvertrag benennen. Rechtsgrundlage sind Art. 37–39 DSGVO und § 38 BDSG. Sie müssen keine Stelle schaffen, bekommen aber sofort Fachwissen und Erfahrung.
Planbare Kosten: Ab 125 € im Monat statt 60.000 bis 90.000 € pro Jahr für eine interne Vollzeitstelle inklusive Weiterbildung und Nebenkosten.
Flexibel bleiben: Ein externer DSB hat keinen Sonderkündigungsschutz. Der Vertrag endet zu den vereinbarten Fristen, bei einem Wechsel sorgen wir für eine lückenlose Übergabe.
Team statt Einzelperson: Hinter Ihrem Ansprechpartner stehen Vertretung, Juristen und Auditoren. Ihr Datenschutz hängt nicht an einer Person.
Who is Proliance's external DPO suitable for?
Ab wann ist ein Datenschutzbeauftragter Pflicht?
Proliance supports companies across the entire DACH region – from growing start-ups to established mid-sized businesses.
Particularly suitable for:
- SMEs (20–500 employees) that legally require a DPO but cannot justify a full-time position
- Companies without in-house compliance expertise looking for a reliable partner
- Companies in regulated industries (health, finance, HR tech) that require industry-specific expertise
- Growing companies that want to implement scalable data protection
- Companies with international ties that need to ensure GDPR compliance for cross-border data processing
In Deutschland müssen Sie einen Datenschutzbeauftragten benennen, wenn eine dieser Bedingungen zutrifft:
Besonders geeignet für:
- In der Regel mindestens 20 Personen beschäftigen sich ständig mit der automatisierten Verarbeitung personenbezogener Daten (§ 38 BDSG).
- Ihre Kerntätigkeit besteht in der umfangreichen Verarbeitung besonderer Datenkategorien, etwa Gesundheitsdaten (Art. 37 DSGVO).
- Sie nehmen Verarbeitungen mit hohem Risiko vor, für die eine Datenschutz-Folgenabschätzung nötig ist, oder verarbeiten Daten geschäftsmäßig zur Übermittlung oder für Markt- und Meinungsforschung.
Auch ohne Pflicht gilt die DSGVO. Ein externer DSB hilft Ihnen, Dokumentation, Informationspflichten und Betroffenenrechte sauber umzusetzen.

When is a Data Protection Officer mandatory?
Ab wann ist ein Datenschutzbeauftragter Pflicht?
In Germany, a Data Protection Officer is legally required in the following cases:
- Ab 20 Personen, die regelmäßig personenbezogene Daten automatisiert verarbeiten (§ 38 BDSG)From 20 individuals who regularly process personal data automatically (§ 38 BDSG)
- When processing special categories of personal data (e.g., health data, biometric data) in accordance with Art. 9 GDPRVerarbeitung besonderer Kategorien personenbezogener Daten (z. B. Gesundheitsdaten, biometrische Daten) gemäß Art. 9 DSGVO
- For the commercial processing of personal data for the purpose of transmission or anonymized evaluationgeschäftsmäßigen Verarbeitung personenbezogener Daten zum Zweck der anonymisierten Übermittlung oder für Markt- und Meinungsforschung
- For certain monitoring measures (e.g., video surveillance, scoring)Überwachungsmaßnahmen (z. B. Videoüberwachung, Scoring)
Ask now for a non-binding consultation offer

Even without a DPO obligation, the GDPR remains binding
What are the advantages of an external Data Protection Officer compared to an internal one?
Welche Vorteile bringt ein externer Datenschutz-beauftragten?
The decision between an internal and external DPO is a strategic one. Here are the key differences at a glance:
Conclusion
What does your external Data Protection Officer handle at Proliance?
Our team of certified DPO experts handles all legally mandated and additional tasks – proactively, not reactively.
Appointment and Formal Designation
Bestellung und Meldung
We handle the legally compliant appointment as an external DPO according to Art. 37 GDPR, including notification to the competent supervisory authority and documentation in the record of processing activities.
Wir übernehmen die formale Benennung nach Art. 37 DSGVO und die Meldung an die Aufsichtsbehörde.
Consulting and Ongoing Support
Laufende Beratung
Your dedicated contact person is available for all data privacy questions – from the introduction of new tools and employee inquiries to communication with authorities.
Ihr fester Ansprechpartner beantwortet Fragen zu Tools, Mitarbeiteranfragen und Behörden.
Data Protection Audits and Risk Analyses
Audits und Risikoanalysen
Regular review of your processing activities, identification of risks, and development of concrete measures – documented and audit-ready in Proliance 360.
Wir prüfen Ihre Verarbeitungstätigkeiten, zeigen Risiken auf und dokumentieren alles auditbereit in Proliance 360.
Training and Awareness
Schulungen
Data protection starts with people. We train your employees – digitally, efficiently, and verifiably – to prevent data breaches from occurring in the first place. → To Data Protection Training
Digitale Datenschutzschulungen für Ihr Team, nachweisbar und effizient.
Support with Data Breaches and Regulatory Communication
Datenpannen und Behörden
In an emergency, every hour counts. We support you with reporting data breaches (Art. 33 GDPR), communication with supervisory authorities, and documenting all measures. → To Data Protection Documentation
Wir unterstützen bei Meldungen nach Art. 33 und 34 DSGVO, bei Behördenkontakt und bei der Dokumentation.
Contract Management and Data Processing
Verträgee und Auftrags-verarbeitung
Review and drafting of Data Processing Agreements (DPAs) in accordance with Art. 28 GDPR – for all service providers who process personal data on your behalf.

Support for Handling Data Subject Requests
Anfragen betroffener Personen
Support in implementing data subject rights: Requests for erasure, access requests, objections, and the withdrawal of consent must be processed accurately and in a timely manner to avoid complaints from supervisory authorities.
Begleitung bei der Umsetzung von Betroffenenrechten, wie u.a. Auskunfts- und Löschanfragen.
Consulting for the implementation of new IT systems and technologies
IT-Systeme und Technologien
When introducing new IT systems or technologies, we help ensure a privacy-friendly design and configuration and know what it takes to legally process data.
What does an external Data Protection Officer cost?
The costs for an external DPO vary depending on company size, industry, and scope of support. As a guide:
Die Kosten hängen von Unternehmensgröße, Branche und Betreuungsumfang ab. Hier sehen Sie unsere drei Pakete.
For comparison:

- 1 user access to the Proliance 360 data protection software
- Consulting hours on request
- Up to 72-hour response time for inquiries
- 1 Zugang der Datenschutz Software Proliance 360
- Beratungsstunden auf Anfrage
- Bis zu 72h Reaktionszeit zu Anfragen

- Additionally, 6 user accounts for the data protection software for functional areas
- A total of 15 consulting hours from our data protection experts (per year)
- Up to 48 hours response time to inquiries
- Zusätzlich 6 Zugänge der Datenschutz Software für Funktionsbereiche
- Insgesamt 15 Beratungsstunden von unseren Datenschutz Experten (pro Jahr)
- Bis zu 48 Stunden Reaktionszeit zu Anfragen

- Unlimited access
- A total of 25 consultation hours with our data protection experts (per year)
- Up to 24-hour response time for inquiries
- Dedicated contact person from our Privacy Team
- Beliebig viele Zugänge
- Insgesamt 25 Beratungsstunden von unseren Datenschutz Experten (pro Jahr)
- Bis zu 24 Stunden Reaktionszeit zu Anfragen
- Persönlicher Ansprechpartner aus unserem Privacy Team
With Proliance, you properly implement data protection
Datenschutz einfach erledigt mit Proliance
Without Proliance
- Legal Risk: Unclear responsibilities, missing documentation, unnecessary vulnerabilities in audits.
- Operational Risk: Data protection falls by the wayside because internal resources are lacking or priorities change.
- Knowledge Risk: Individual knowledge, dependence on one person, high onboarding and training burden.
- Communication Risk: Friction between departments, IT, HR, and management – with no neutral mediator.
- Cost Risk: Unpredictable expenses due to training, absences, and ad-hoc consulting.
Ohne Proliance
- Rechtliches Risiko: Unklare Zuständigkeiten, fehlende Nachweise, unnötige Angriffsflächen in Audits.
- Operatives Risiko: Datenschutz bleibt liegen, weil interne Ressourcen fehlen oder Prioritäten wechseln.
- Know-how-Risiko: Einzelpersonenwissen, Abhängigkeit von einer Person, hohe Einarbeitungs- und Schulungslast.
- Kommunikationsrisiko: Reibung zwischen Fachbereichen, IT, HR und Geschäftsführung – niemand moderiert neutral.
- Kostenrisiko: Schwer planbare Aufwände durch Weiterbildung, Ausfälle und Ad-hoc-Beratung.
With Proliance
- Team of Experts, not an Individual: Your contact person is backed by a team – ensuring backup and integrated software and consulting from a single source: Proliance 360 consolidates tasks, documents, and evidence – immediately audit-ready.
- Proactive, not reactive: We provide timely updates on changes, rulings, and specific actions required.
- Industry Expertise: Hands-on expertise from regulated industries – understandable, actionable, without buzzwords.
- Transparent Collaboration: All activities and recommendations are transparently documented – no black box.
Mit Proliance
- Experten-Team statt Einzelperson. Ihr Ansprechpartner hat ein Team im Rücken, auch bei Urlaub und Krankheit.
- Software und Beratung aus einer Hand. Proliance 360 bündelt Aufgaben, Dokumente und Nachweise, damit Sie jederzeit auditbereit sind.
- Proaktiv statt reaktiv. Wir informieren Sie frühzeitig über Gesetzesänderungen, Urteile und konkreten Handlungsbedarf.
- Transparent. Alle Aktivitäten und Empfehlungen sind nachvollziehbar dokumentiert. Sie sehen jederzeit Ihren Datenschutz-Status.
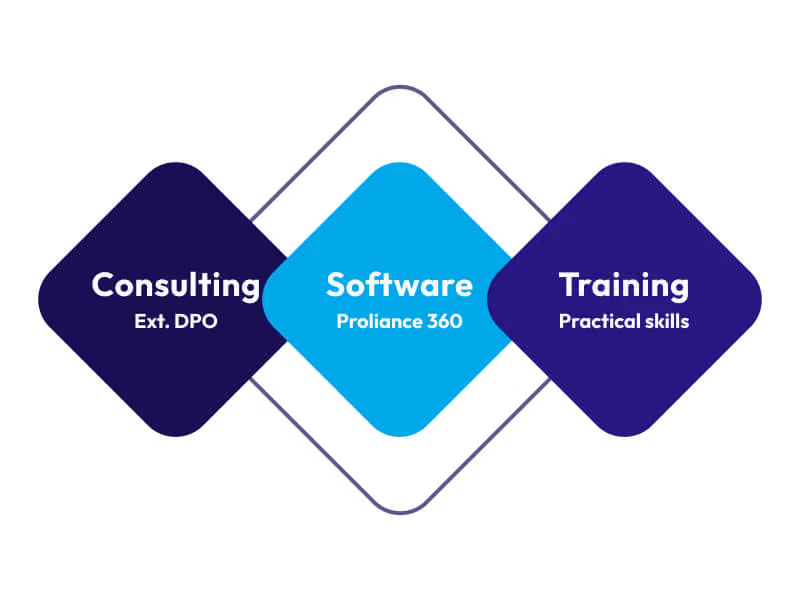
Holistic instead of piecemeal – our data protection portfolio
After the initial assessment, it's not just about 'somehow being GDPR compliant,' but about maintaining compliance permanently: with clear responsibilities, verifiable documentation (e.g., VVT, TOMs, data processing agreements), regular training, and a system that doesn't forget updates and tasks.
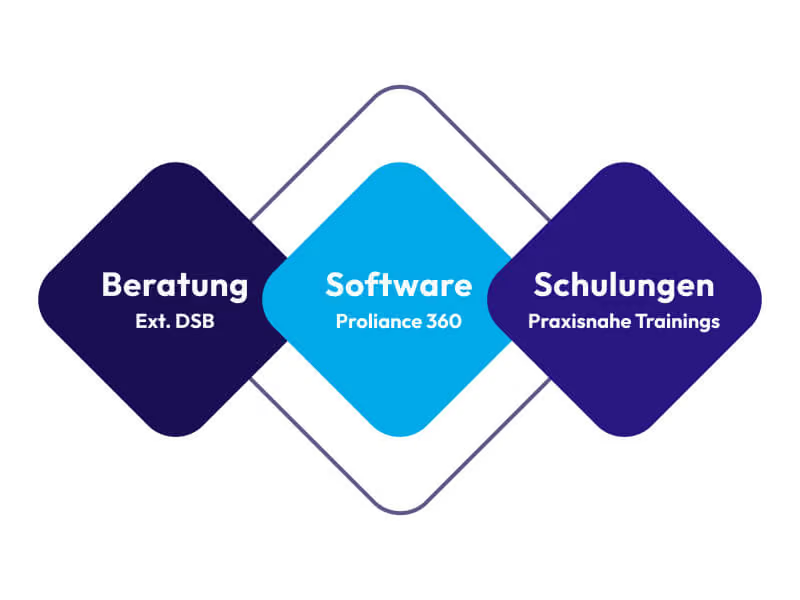
Ganzheitlich statt Stückwerk – unser Portfolio für Datenschutz
How working with Proliance works


Efficient data protection starts here. We'll show you how.
What to expect in the initial consultation:
- Analysis of Your Current Data Privacy Situation
- Clarification of Legal Obligations for Your Company
- Specific Offer for Your External DPO
What 3.000+ Companies Value Most About Proliance



Frequently asked questions always need good answers. Here they are.
In serious cases – such as a data breach – we assist you with reporting in accordance with Art. 33 GDPR, communicating with the competent supervisory authority, informing affected individuals as per Art. 34 GDPR, and thoroughly documenting all actions. We also support you during official audits, for instance, following a complaint from an affected individual.
Pricing is based on company size, industry, and the scope of services required. For SMEs, packages start at €125 per month. Get a personalized quote during a free initial consultation.
Yes. Unlike an internal DPO, an external DPO does not have enhanced protection against dismissal. The contractual relationship can be terminated in accordance with the agreed terms. Proliance ensures a seamless handover.
Article 37(5) of the GDPR requires that the DPO must possess expert knowledge in data protection law and practice. All Proliance DPOs are certified (TÜV, GDD, or comparable) and continuously develop their expertise. They are supported in their work by a team of lawyers and auditors.
The service is commissioned through a written service contract. Proliance then handles the notification to the competent supervisory authority and the documentation in the record of processing activities – fully and in a legally compliant manner.
The internal DPO is an employee of the company, while the external DPO is an independent service provider. An external DPO offers specialized expertise, legally guaranteed independence, and a team of experts supporting them – all without special termination protection and without the costs of a full-time employee.
In Germany, a Data Protection Officer (DPO) is legally mandatory for organizations with 20 or more individuals who regularly process personal data automatically (§ 38 BDSG). Furthermore, a voluntary appointment can be beneficial to minimize liability risks.