ISO 27001 Consulting

Achieve certification on your first attempt with clear processes

Save time and resources on your ISO 27001 certification: our consultants guide you through every step with industry expertise, clear priorities, and support from a modern ISMS platform.

  • Up to 70% less effort
  • Up to 40% lower costs
  • 100% success rate in ISO 27001 audits
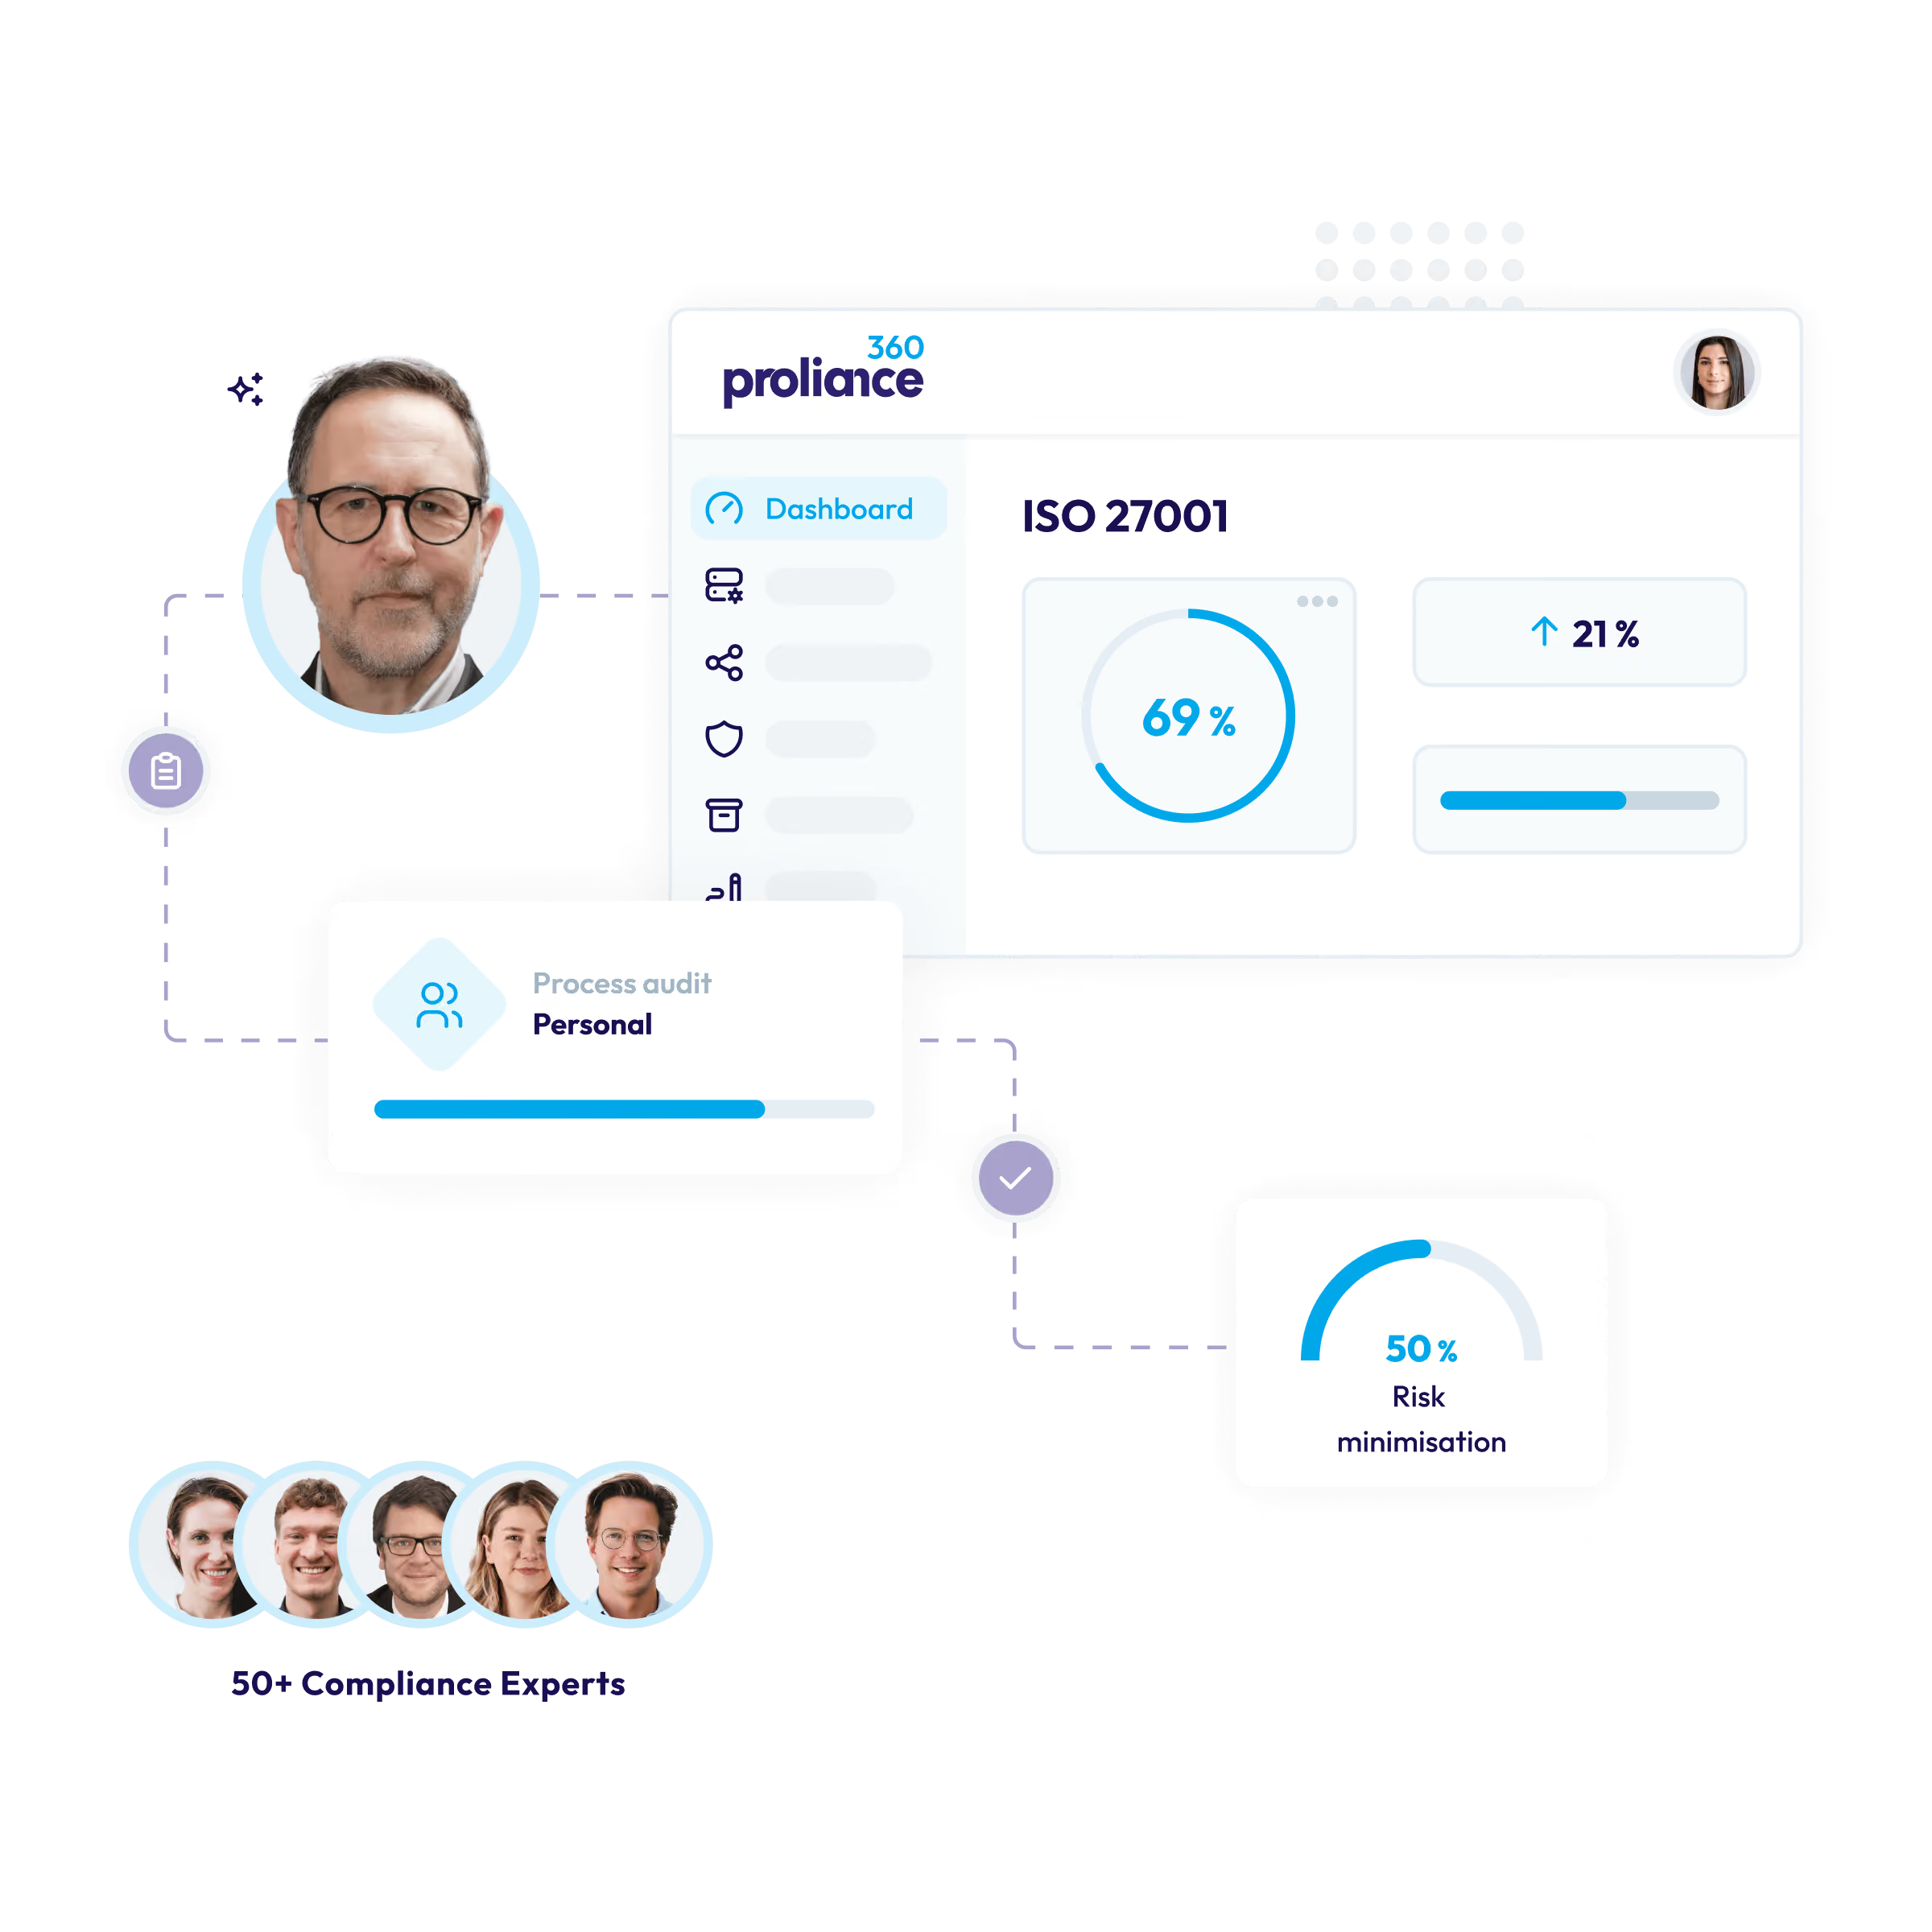
Dashboard shows ISO 27001 with 69% progress and 50% risk minimization, plus photos from compliance experts.
Hosting in Europe
Platform-based consulting
50+ TÜV and DEKRA certified experts
Compliance. Done Safely.
Why Proliance?

Efficient ISO 27001 Consulting: Secure Your Certification with Proliance 

The traditional approach without a partner

  • Significant Effort, as Internal Expertise Must First Be Developed
  • Time and Staff Shortages Due to Complex Requirements
  • High Risk: Manual management in Excel & co. jeopardizes success in the audit.
  • Fragmented Process if No Central Tool is Available

The Smart Way with Proliance

  1. External Consultants Bring Expertise and Industry Knowledge
  2. Approximately 50% Time Savings Through Clear Guidance and Priorities
  3. Increased Acceptance Thanks to Transparency and Awareness Training
  4. 100% Success Rate – All our customers have passed on their first attempt so far
  5. Process Overview with a Central Platform and Clear Workflows
Do I need ISO consulting?

You are in the right place if…

you need to protect sensitive information or customer data
A structured ISMS helps you systematically protect confidential information, identify risks early, and embed appropriate security measures within your company.
you want to gain a competitive advantage
ISO 27001 certification builds trust, opens up new opportunities, and helps you stand out from the competition by demonstrating your commitment to security.
You lack the capacity for ISMS implementation
With clear processes, digital workflows, and practical support, you can reduce internal effort and implement your ISMS efficiently, even with limited resources.
ISO 27001 is an important signal of trust in your industry
ISO 27001 certification strengthens your credibility with customers, partners, and in tender processes, demonstrating that information security is implemented in a measurable way within your company.
you want to avoid costs from data breaches or fines
An effective ISMS helps you prevent security incidents, reduce follow-up costs, and reliably comply with regulatory requirements.
Customers, suppliers, or regulators are requiring you to implement an ISMS
When external demands increase, an ISMS provides the necessary structure to demonstrate compliance, meet expectations, and establish sustainable security standards.
NIS2, DORA, or TISAX® are relevant to you
An ISMS provides the robust foundation needed to implement regulatory requirements effectively and prepare your company for future audit and compliance obligations.
you are unsure about the costs and effort involved in certification
With clear processes, digital workflows, and personal guidance, ISO 27001 becomes predictable, efficient, and economically viable to implement.
Schedule an ISO 27001 consultation

Request a no-obligation consultation for ISO 27001 now
Data protection and information security can seem overwhelming at first glance. Our experts are always here to help. Get a free consultation and receive a no-obligation recommendation for your next steps.
100+ Experts
Book a consultation
Ein lächelnder Mann mit kurzen braunen Haaren sitzt in einem weißen Hemd auf einem Stuhl vor einem Fenster.
Your Benefits

How external ISO 27001 consulting relieves your company and improves your processes

50
%
Risk minimization
Our experts support you in building an ISMS solution that effectively minimizes your risks.
100
%
Success rate for certifications
To date, all clients have passed the external ISO 27001 audit on their first attempt after our consultation.
3-12
Months until audit
Solid experience, deep industry knowledge, and practical recommendations efficiently help you achieve your goals.
50
+
TÜV & DEKRA certified experts
You benefit from personalized support from experts with proven expertise.
3000
+
Customers
From client projects, we understand the challenges of various industries – including yours.  
Predictable
through transparent costs
Before we advise you, you'll know exactly what services to expect and at what price.
customer experiences

What 3.000+ Companies Value Most About Proliance
In our healthcare industry, data privacy is a top priority. We are constantly challenged by the ever-increasing demands for data protection and information security. Proliance helps us find quick and tailored solutions.
We were looking for a partner who could take tasks off our plate and genuinely support us with advice and practical help. When we ask a question, the Proliance experts quickly provide a clear, actionable answer. The GAP analysis was a valuable reality check. Not because we were in an uncertain position, but because it showed us where we could further refine our processes and documentation more strategically.
We were looking for a professional, comprehensive data privacy solution. With Proliance, we are in good hands and receive comprehensive advice!
We have been implementing our annual data protection training through Proliance for years – this provides us with a clearly structured framework for knowledge transfer. Particularly with the use of AI in our teams, we specifically supplement the training where new requirements emerge. This ensures that responsibilities, risks, and legal frameworks remain transparent.
In our healthcare industry, data privacy is a top priority. We are constantly challenged by the ever-increasing demands for data protection and information security. Proliance helps us find quick and tailored solutions.
Proliance helped us take our company's data protection to the next level. The team's expertise and quick responsiveness supported us every step of the way. Highly recommended.
6 steps to certification

How ISO 27001 consulting works at Proliance

A typical ISO 27001 consulting project follows six steps. The core focus is on establishing or auditing your Information Security Management System (ISMS). Upon request, we can provide support beyond the certification process. The duration of the consulting depends on your starting point: small companies with clear structures are generally ready for the audit process in 3 to 6 months, while larger organizations typically take 6 to 12 months.

01 - Initial consultation & gap analysis

Analysis of your status quo compared to the ISO 27001 standard. (Month 1)

02 - Project planning & ISMS implementation

Development and integration of a tailored ISMS with the help of our certified ISO 27001 consultants, prioritized according to your resources and requirements. (Month 2)

03 - Documentation creation

Creation of all relevant policies, procedures, and evidence. (Month 3)

04 - Employee Training

Creation of all relevant policies, procedures, and documentation. (Month 4)

05 - Internal Audits & Audit Preparation

Preparation for external certification through audits and checks, including proven recommendations for an efficient path to certification. (Month 5)

06 - Certification Support

Support during the audit process from certified consultants. (Month 6)

07 - Long-term Support

Continuous ISMS optimization, advice on updates, and support for annual reviews. (from Month 7)

Relevant Companies

Is ISO 27001 certification beneficial for your company?

Certification is worthwhile for all companies that want to increase the trust of customers, partners, and suppliers. Especially in the supply chain, business partners often specifically demand certification to ensure security within the supply chain.
Large enterprises
Obligation by laws or industry standards
SMEs
Competitive advantage and improvement of security standards
Technology providers
Protection of intellectual property and customer data
Financial service providers
Compliance with regulatory requirements
Healthcare
Ensuring patient data confidentiality
Suppliers
A Mark of Supply Chain Security and a Complement to TISAX®
The Standard at a Glance

Core Components of the ISO Standard and the Impact of Implementation

| ISO Requirements | Benefit with ISO 27001 Implementation | | :--- | :--- | | Definition and documentation of security policies and procedures | Security and efficiency through clear processes | | Clear assignment of tasks and responsibilities for information security | Accountability, as everyone in the company knows their role | | Identification, assessment, and treatment of risks | Systematic protection against cyber threats and minimization of business risks | | Implementation and monitoring of security measures | Demonstrable trust for customers and partners as well as compliance with regulatory requirements | | Regular training and awareness measures for employees | Strong security culture and reduced risk from human error | | | |
Arrange a consultation

Ask now for a non-binding consultation offer

Data protection and information security can seem overwhelming at first glance. Our experts are always happy to help you. Get free advice and receive a non-binding recommendation on your next steps.
100+ Experts
Book a consultation
Ein lächelnder Mann mit kurzen braunen Haaren sitzt in einem weißen Hemd auf einem Stuhl vor einem Fenster.
Holistic Information Security

Support that goes beyond ISO 27001 consulting 

Are your challenges significant, but your internal resources scarce? Beyond ISO 27001 consulting, we offer one-stop support for related topics.

Frameworks for your company

ISO 27001 is just the beginning

Is your ISMS successfully certified according to ISO 27001? Then your processes are ready to be optimized for further standards. Whether NIS2, ISO 9001, or TISAX® – we support you with consulting and our ISMS platform.  
Frequently Asked Questions

Still have questions? We have the answers.

Is ISO 27001 mandatory?

The ISO 27001 standard is not legally mandated in Germany. However, in certain industries (e.g., critical infrastructure, finance, healthcare), it can effectively become a prerequisite for contracts or legal compliance.

What is an ISMS according to ISO 27001?

An ISMS (Information Security Management System) based on ISO 27001 is a structured framework of processes, policies, and measures for the systematic protection of sensitive information. It helps organizations identify, assess, and effectively mitigate risks.

How much does ISO 27001 consulting cost?

The cost of ISO 27001 consulting varies depending on company size, current situation, and the desired scope of services. For small businesses, projects start from approximately €5,000 – €10,000; for more complex structures, costs can be higher. We would be happy to provide you with a customized offer.

What requirements does my company need to meet?

Any company can become ISO 27001 certified. The prerequisites are: management commitment, resources for planning, implementation, and documentation, and a commitment to continuous improvement. Our ISO 27001 consultants will help you meet all requirements.

What are the costs for ISO 27001 certification?

For SMEs, external audit costs range between 10,000 and 25,000 Euros, depending on the number of employees, locations, and complexity. A small software agency with 25 employees pays approximately 8,000 to 11,000 Euros, while a medium-sized company with 120 employees and two locations pays 18,000 to 24,000 Euros. Annual surveillance audits cost approximately 30 to 40 percent of the initial sum. Proliance minimizes re-audit risks through thorough preparation and shortens the path to certification.

How is Proliance's ISO 27001 consulting structured?

Our ISO 27001 consulting includes:

  • As-Is Analysis & Gap Assessment
  • Planning & Establishment of the ISMS
  • Training & Documentation
  • Internal Audits & Audit Preparation
  • Support throughout the Certification Process

Upon request, we also offer long-term support.

How long does ISO 27001 consulting with Proliance take?

The timeframe depends on the initial situation. For small companies with clear structures, implementation can take 3–6 months. For larger organizations, the certification process usually takes 6–12 months.

What ISO 27001 requirements does my company need to meet?

ISO 27001 requirements include establishing an ISMS, risk assessments, security policies, internal audits, and continuous improvement. Proliance guides you systematically through all requirements – from the initial GAP analysis to successful certification.