Compliance for IT and software companies
Your customers demand ISO 27001, data processing agreements and robust proof of security. Proliance 360 combines software with an external data protection officer and expert consultancy – no need for an in-house compliance team.








What compliance does an IT or software company need?
Protect customer data. Demonstrate security. Use AI responsibly.
IT and software companies process customer data on behalf of others and must demonstrate GDPR-compliant data protection. This is in addition to information security – usually ISO 27001, or SOC 2 or TISAX depending on the client base – as well as AI governance and whistleblower protection. NIS2 obligations are part of information security and apply where relevant.
When compliance suddenly becomes urgent for IT companies
Compliance usually starts with a specific event. Do you recognise your situation?
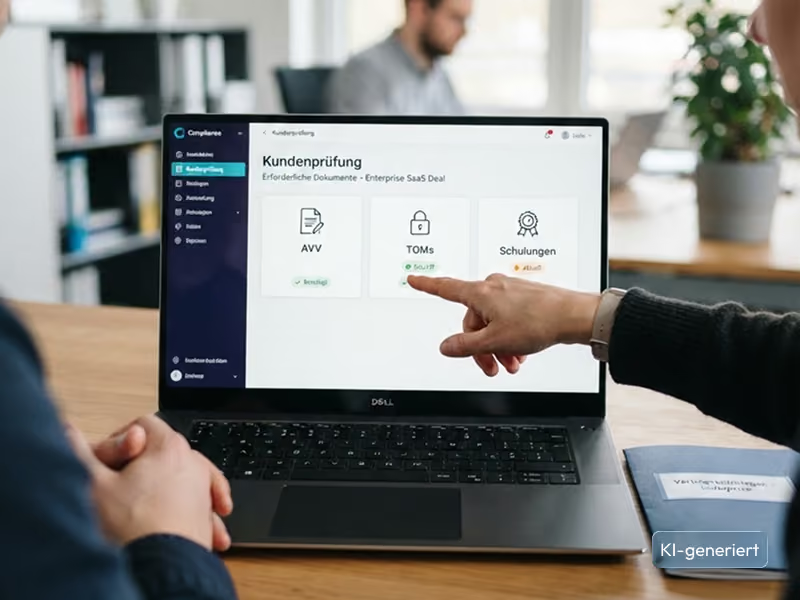
Four topics. One clear path to robust evidence.
From initial customer screening to audit: we connect requirements with what your business truly needs.
Data Protection
Data protection for IT service providers and software vendors
As a data processor, you have obligations to both your clients and the supervisory authorities. We take care of the tasks that often fall by the wayside in day-to-day business – providing clear recommendations instead of more Excel spreadsheets.
External Data Protection Officer - Certified experts advise you, review your documentation and prioritise what needs to be done. Find out more. Find out more
Cohesive documentation - Centrally manage your records of processing activities, sub-processors and contracts. Provide regular, verifiable training for your employees. Find out more
Prepared for the next data protection audit.
- Record of processing activities - Record processing activities in a transparent manner.
- DPA under Art. 28 GDPR - Templates, contract review and documentation.
- TOMs under Art. 32 GDPR - Provide evidence of technical and organisational measures.
- Training records - Document data protection expertise within the team.
Information security: ISO 27001, SOC 2, TISAX and NIS2
Which certification do your customers require? We identify the appropriate standard and implement only what is necessary to achieve it. ISO 27001 is the established ISMS standard for European enterprise clients. SOC 2 is often relevant for US-oriented customers, while TISAX is essential for suppliers in the automotive industry. We incorporate NIS2 based on your specific requirements and supply chain obligations.


More Solutions

KI-Governance und EU AI Act
Klare Regeln für KI in Entwicklung, Support und Vertrieb – und für KI in Ihren Produkten.
- KI-Richtlinie und Freigabeprozess: erlaubte Tools und Daten definieren.
- KI-Inventar, Risikoklasse und Rolle als Anbieter oder Betreiber klären.
- KI-Kompetenz nach Art. 4 mit Schulung und Teilnahmenachweis stärken.
- Auftragsverarbeitung, Datenabfluss und Transparenz prüfen.
Whistleblower protection, reliably organised. For 50 or more employees
In this case, companies are required to establish an internal reporting channel in accordance with the Whistleblower Protection Act. You can use a digital whistleblowing system or have the reporting channel operated externally.
- Set up
- Document
- Operate
We assist with the setup, document the processes and support data-compliant operation.


Compliance that matters to you and works in practice
We create bespoke service packages tailored to your company size, processes, and goals. Together, we implement data protection, information security, whistleblower protection, and AI governance in a way that is legally compliant, clear, and practical for your day-to-day operations.



Compliance certification for your clients. Without the need for an in-house compliance team.
Frequently asked questions about compliance in IT and software companies
Start by creating a record of processing activities, enter into data processing agreements with clients and service providers, define technical and organisational measures, and train your staff. An external data protection officer and a centralised platform make documentation and compliance easier to manage.
It is not a legal requirement for every company. In practice, however, many enterprise clients require proof of information security, and ISO 27001 is the most widely recognised standard for this.
European clients usually ask for ISO 27001, while US-oriented clients more frequently request SOC 2. Clarify this with your key customers before you invest. We can help you decide which is right for you.
This depends on your industry, company size, and the services you offer. IT service providers, managed service providers, and digital service providers are among the groups typically covered. Our NIS2 check provides clarity.
Obligations depend on your role (provider or deployer) and the risk classification of the AI system. All companies using AI are required to ensure their employees possess AI literacy.
An internal reporting channel is mandatory for companies with 50 or more employees. You can use a digital system or outsource the operation of the reporting channel.
Proliance provides consultancy for IT and software companies on data protection, information security, AI governance, and whistleblower protection. Our services include the Proliance 360 platform and the provision of an external data protection officer supported by expert advice.