360° healthcare compliance - Data protection, information security, and AI governance from a single source
Proliance is the specialized compliance partner for healthcare facilities in the DACH region. Whether you run a medical practice, nursing service, or clinic, we cover all regulatory requirements—GDPR, NIS2, ISO 27001, and AI governance—with over 300 healthcare facilities under our care, certified experts, and a platform that actually works in daily practice.




Healthcare compliance: Why self-management fails
Patient data is subject to extremely strict protection (Art. 9 GDPR). Cyberattacks on nursing homes and clinics are rising rapidly. Anyone handling these responsibilities as an afterthought risks existential fines and loss of reputation.
Without Proliance (bureaucratic chaos)
- Overwhelmed by regulations - Obligations such as GDPR, NIS2, and the EU AI Act are managed in parallel, leading to duplicated work and security gaps.
- Cyberattacks endanger patients - A lack of IT security concepts can paralyze operations in an emergency and directly endanger human lives.
- No in-house specialists - Data protection and information security are often handled "on the side" by administrative staff without proper training. This creates a significant liability risk.
With Proliance (all-inclusive protection)
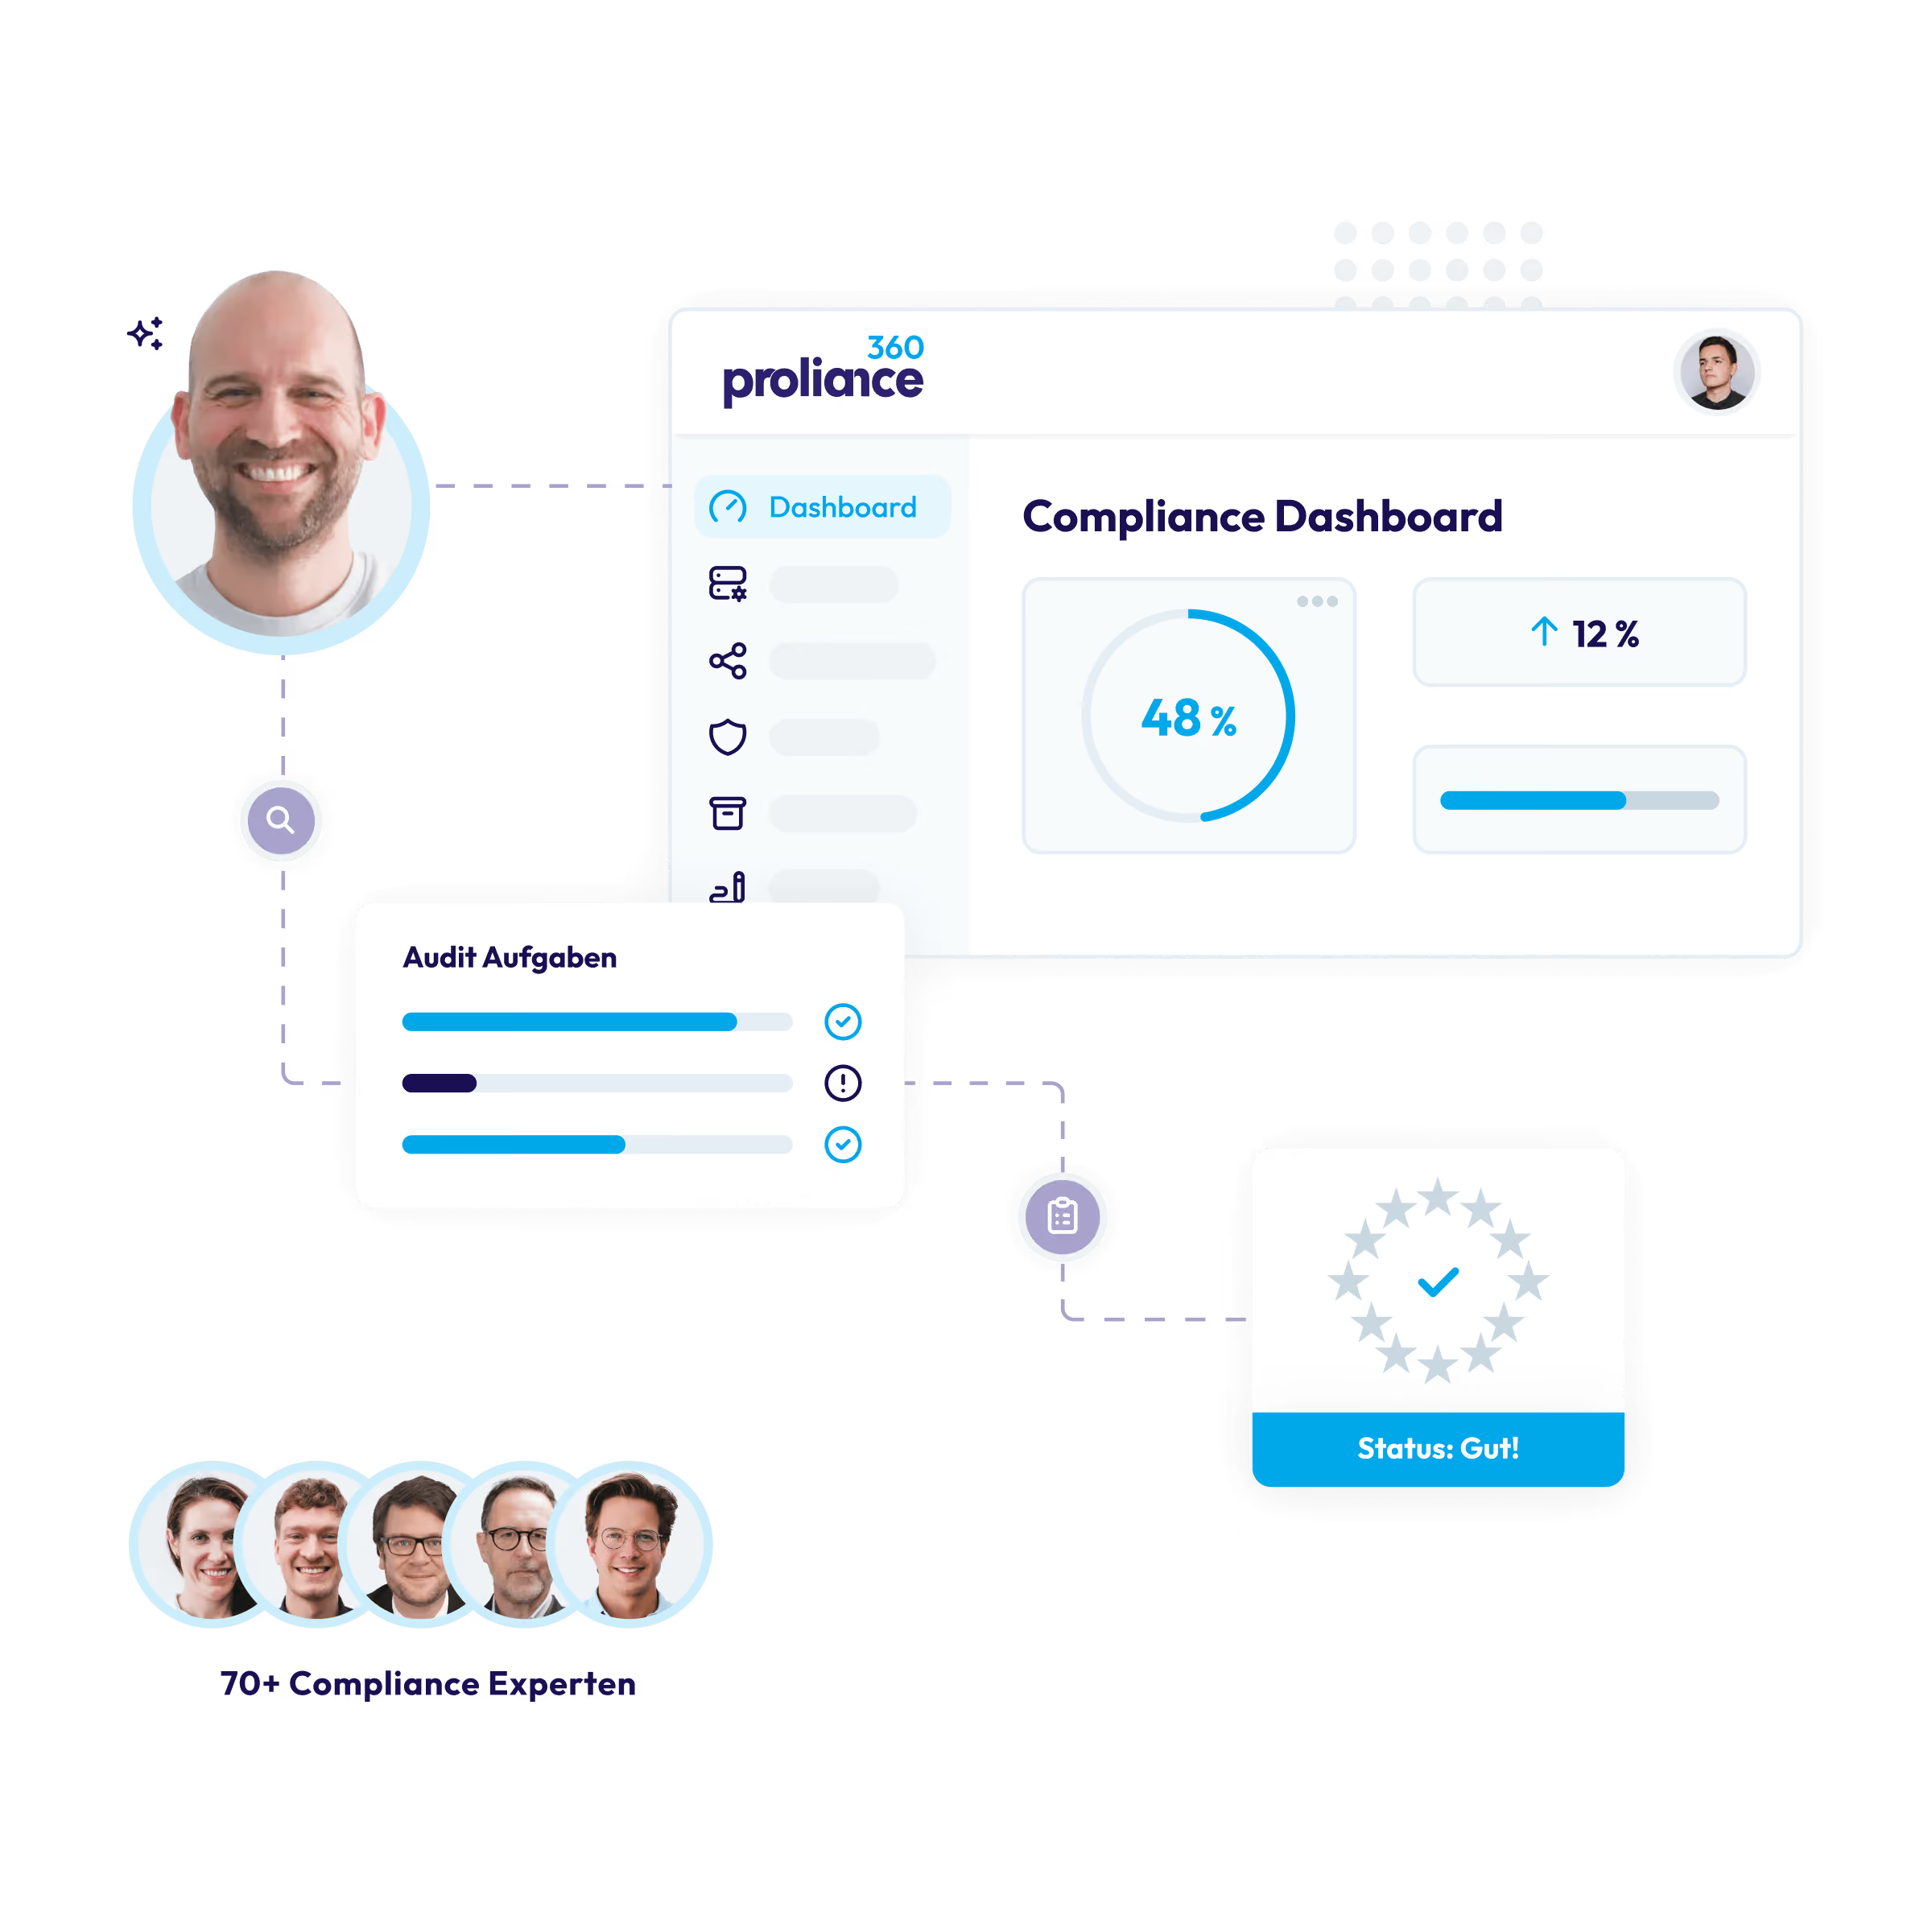
- 3 pillars from a single source - Data protection (GDPR), information security (NIS2, ISO 27001), and AI governance perfectly combined.
- TÜV & DEKRA experts by your side - Over 50+ certified data protection and information security experts are available to advise you.
- Smart Proliance 360 Platform - All policies, training, and documentation managed in one central, audit-proof location. Hosted in the EU.
Healthcare compliance is not a one-size-fits-all topic
The regulatory requirements for a local medical practice differ fundamentally from the complex critical infrastructure rules of a hospital network. We have the right answer for every focus.



Over 300+ healthcare facilities trust Proliance



Mastering the 5 key pillars of compliance
We cover all regulatory requirements in a structured way, so you don't have to worry about liability during audits or inspections.
Frequently asked questions about data protection audits
Hospital networks and MVZ structures require central governance: uniform ISMS guidelines, shared responsibility models, consolidated risk registers, and multi-tenant GRC tools. Clarify responsibilities for shared IT systems and data processing agreements. Proliance 360 offers multi-tenant architecture for network structures with central reporting and local implementation autonomy. More information: Data Protection in Healthcare for care facilities within a network.
Digital Health Applications (DiGA) must comply with high data protection and information security standards according to DiGAV and Section 139e SGB V: end-to-end encryption, data minimization, consent management, and GDPR-compliant data processing agreements. The BfArM reviews these requirements in a fast-track procedure. Proliance offers DiGA audits, gap analyses, and documentation templates.
Recommended Certifications: ISO 27001 (Information Security), ISO 27701 (Privacy Extension), Certification according to TISAX® (Automotive Suppliers), KRITIS-B3S (Healthcare Industry Standard). Proliance accompanies clients from the ISO GAP analysis, through the step-by-step ISMS development, to audit preparation. Combine the ISO 27001 Consulting with GDPR Consulting for dual compliance assurance.
The NIS2 directive mandates stricter cybersecurity measures for healthcare facilities, classified as critical infrastructure (KRITIS). These include risk analyses, incident response plans, reporting obligations for security incidents, and regular audits. Hospitals must demonstrate technical and organizational measures (TOM) by autumn 2024. Proliance 360 supports with NIS2 readiness checks, automated risk assessments and compliance dashboards. Combine NIS2 with GDPR requirements in healthcare for comprehensive protection.
Yes! Modern GRC platforms automate: risk assessments via questionnaires, task workflows, deadline monitoring (GDPR deletion periods, NIS2 reporting obligations), document generation (RoPA, TOM documentation), and dashboards for management. This saves 60–70% of manual work. Proliance 360 integrates data protection and information security in one platform with AI-powered suggestions.
Knowledge on data protection, information security, and AI compliance: guides, templates & magazine
Magazine


Guides & Reports
Data Protection Templates
Compliance in your facility – simple, secure, and from a single source.