Data Protection, Information Security, and AI Governance for Industry & Manufacturing
GDPR, NIS2, ISO 27001, and the EU AI Act - industrial companies are under triple regulatory pressure. Proliance bundles all requirements into one platform, with personal experts who know your industry.




Why industrial companies trust Proliance
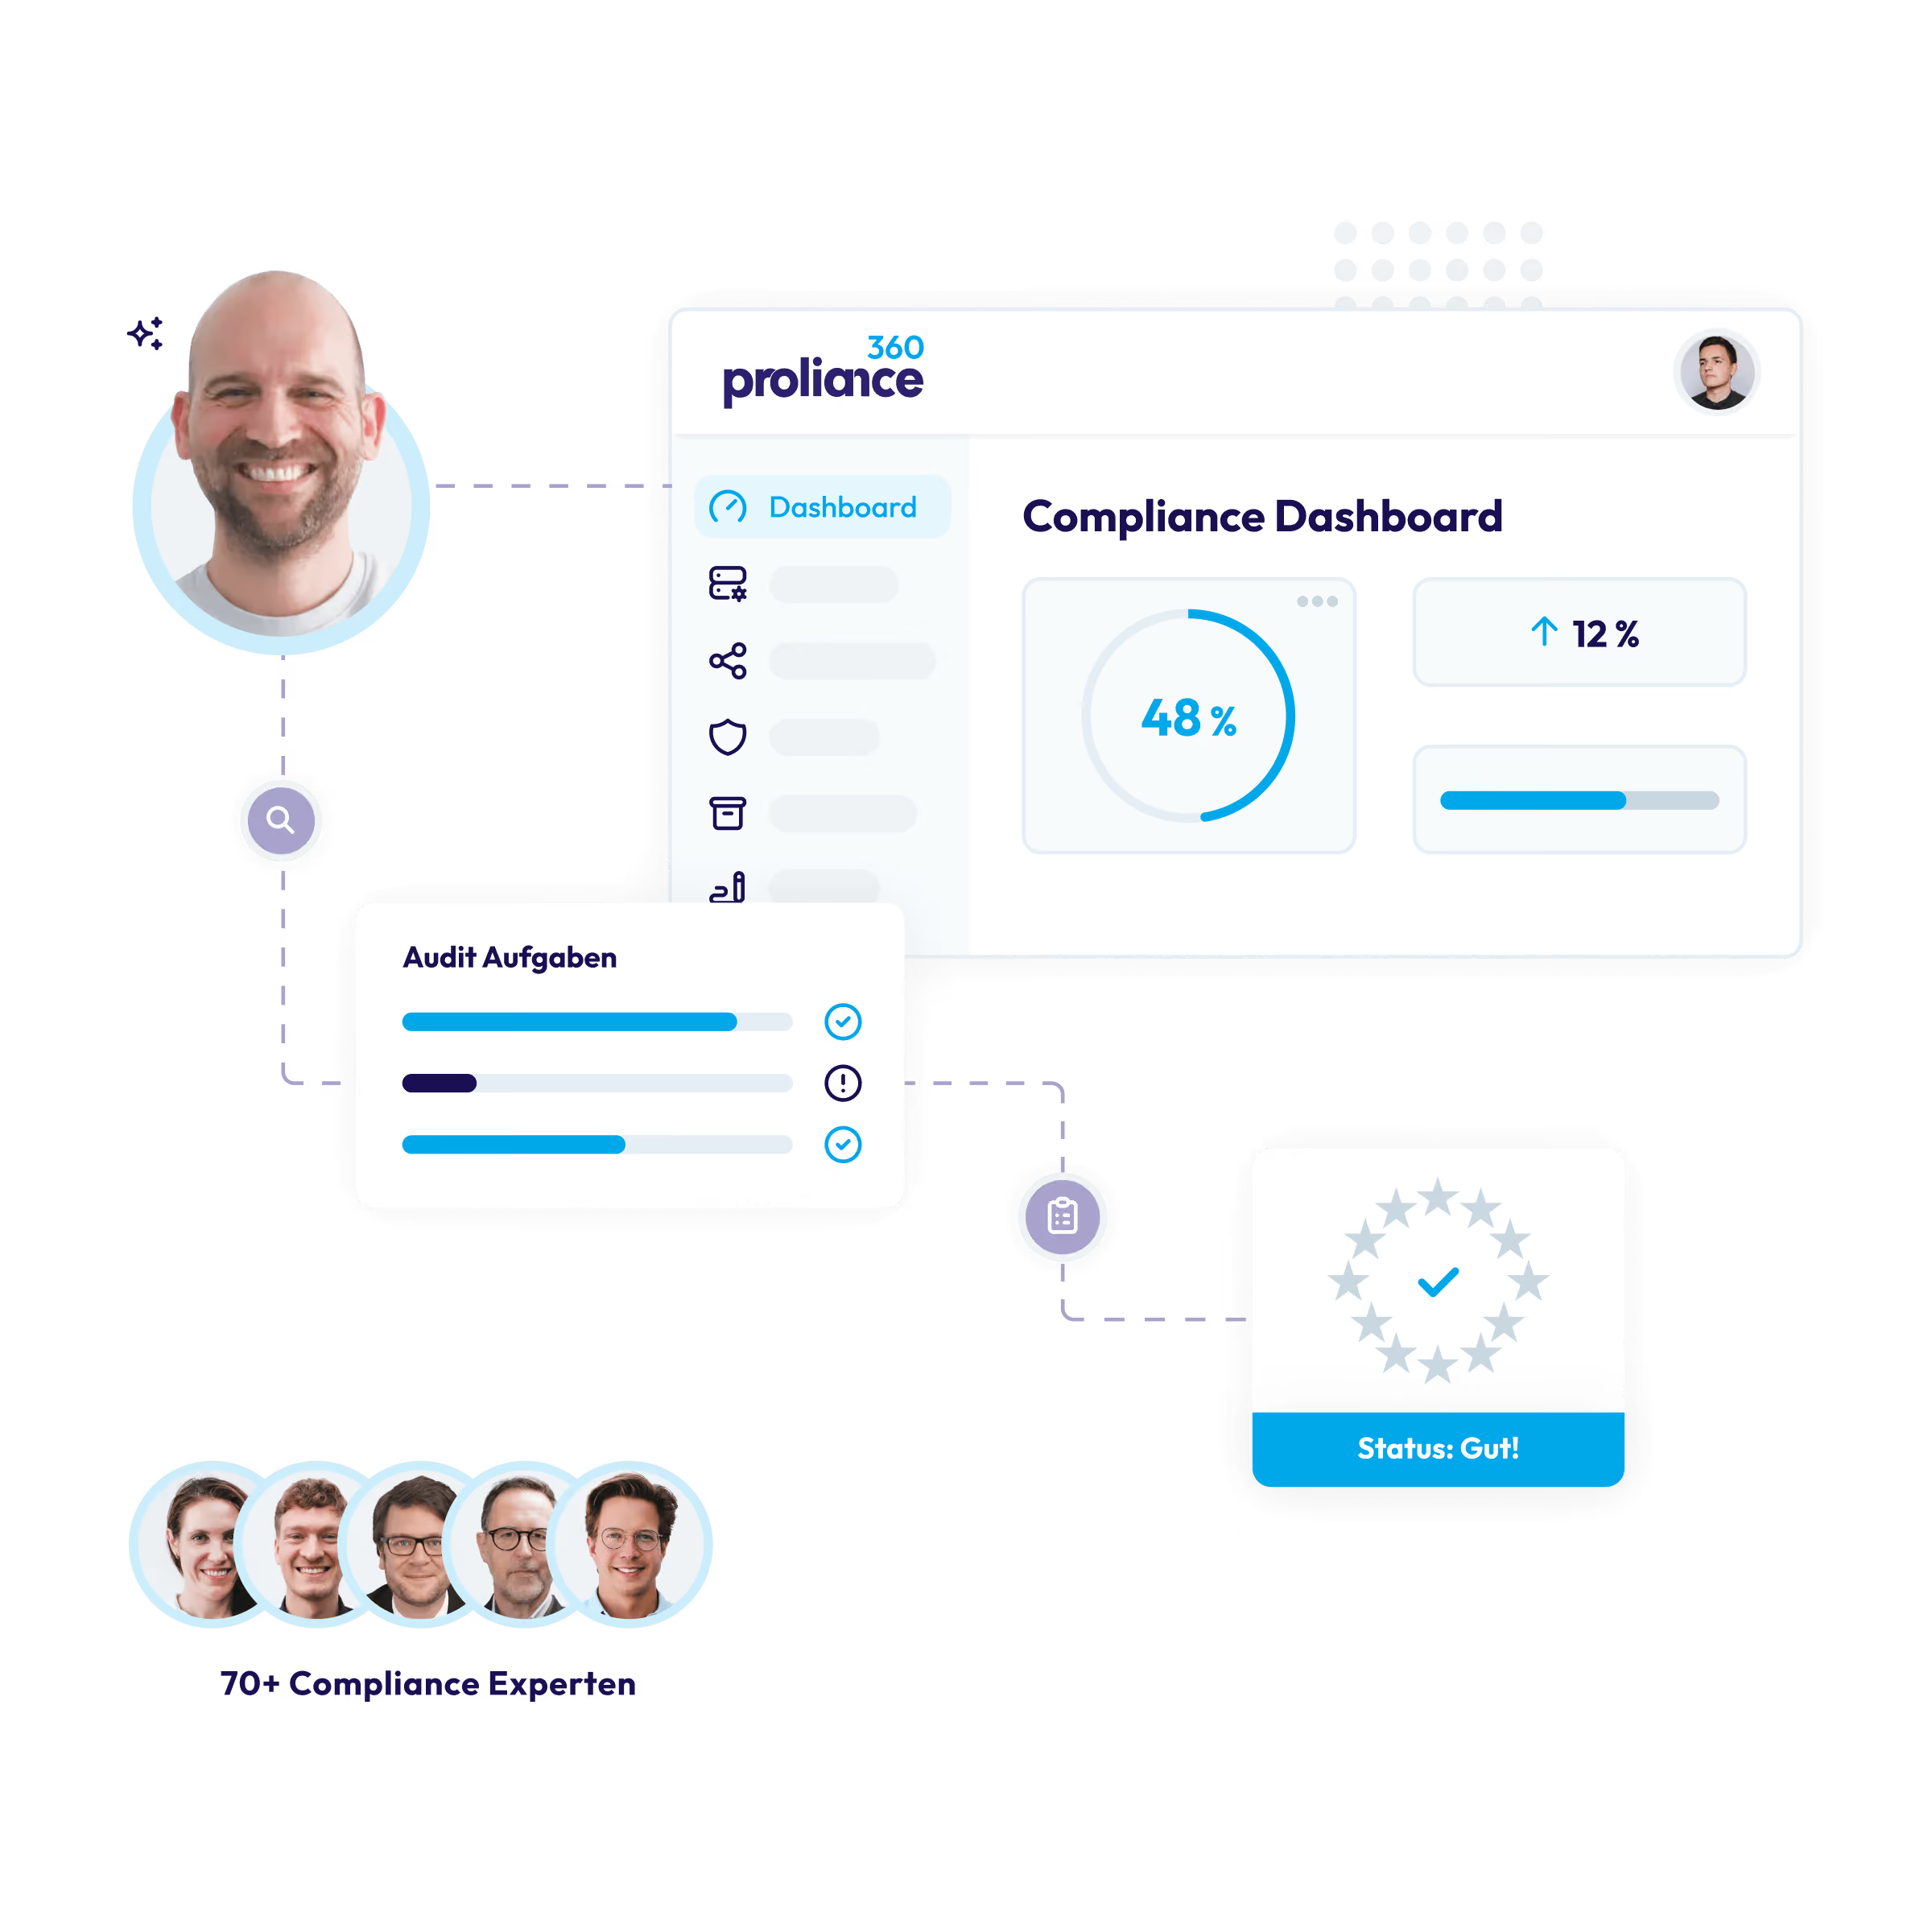
What does it actually mean to manage compliance in an industrial company without support? Proliance covers all three core industrial compliance topics - in one platform, with a dedicated team of experts.
Without Proliance
- Data protection, information security, and AI compliance are managed by different service providers - leaving you without a unified overview.
- Records of processing activities and ISMS documentation are maintained manually in Excel - making them error-prone and risky during audits.
- Legislative changes (NIS2, EU AI Act) are implemented late or not at all - creating liability risks for management.
- There is no structured process for data breaches - leading to missed or late reporting obligations.
- Employee training is conducted inconsistently - leaving you without the necessary documentation for audits.
- ISO 27001 or NIS2 certifications are delayed due to a lack of a clear roadmap - resulting in lost business.
- AI systems in production are being operated without risk classification—risking EU AI Act violations.
With Proliance
- Data protection, information security, and AI governance in one platform—a personal contact for all topics.
- Record of processing activities, ISMS documentation, and AI registers, centralized and structured—audit-ready at all times.
- Automatic updates on legislative changes—your experts inform you proactively before deadlines expire.
- Clear process for data breaches and reporting obligations—documented and on time.
- Digital employee training with certificates and complete training history—audit-proof and verifiable.
- Structured ISO 27001 and NIS2 support with a clear roadmap—turning certifications into a competitive advantage.
- AI risk classification and documentation according to the EU AI Act—legally compliant AI deployment in production.
Why data protection and information security in the industrial sector are more complex than in other industries
Machine data, production processes, supply chains, and AI systems—industrial companies process sensitive data on many levels simultaneously. This creates regulatory requirements that go far beyond standard GDPR.
Data Protection, Information Security, and AI Governance for Industrial Companies
Proliance covers all three core industrial compliance topics—in one platform, with a dedicated team of experts.



Customer Reviews: Industrial companies on Proliance
Three neutral placeholder reviews for the new section - without real customer names, companies, or unsubstantiated ratings.




Frequently asked questions about data protection and compliance in the industry
Industrial companies are subject to the GDPR and are required, among other things, to maintain a record of processing activities (ROPA), enter into GDPR-compliant data processing agreements with service providers, document technical and organizational measures (TOMs), and provide regular staff training. Furthermore, appointing a data protection officer is mandatory for companies with 20 or more employees who regularly work with personal data.
NIS2 applies to companies of a certain size within specific sectors. In the industrial sector, this primarily affects businesses involved in the production of critical goods (chemicals, food, mechanical engineering), logistics, and manufacturing—provided they have more than 50 employees or an annual turnover exceeding 10 million euros. Suppliers to critical infrastructure may also be indirectly affected.
The EU AI Act classifies AI systems according to risk levels. AI applications in production—such as those used for quality control, predictive maintenance, or automated decision-making regarding employees—can be categorized as high-risk AI. This entails documentation obligations, conformity assessments, transparency requirements, and the assurance of human oversight. Proliance supports you with risk classification and implementation.
Proliance supports industrial companies throughout their entire journey to ISO 27001 certification: from the initial gap analysis and the implementation of an Information Security Management System (ISMS) to audit preparation and support. Our certified auditors understand the specific requirements of the industry—from production security to supply chain compliance.
An external data protection officer is generally mandatory for companies with 20 or more employees who regularly process personal data. In manufacturing, this is almost always the case due to employee, customer, and supplier data. Compared to an internal appointment, an external DPO offers the advantages of independence, specialized expertise, and cost-efficiency.
Guides and resources for data protection and compliance in the industrial sector
Magazine


Guides & Reports
Data Protection Templates
Compliance. Handled securely – even in the industrial sector.