
Data protection, information security and AI compliance for energy suppliers and municipal utilities
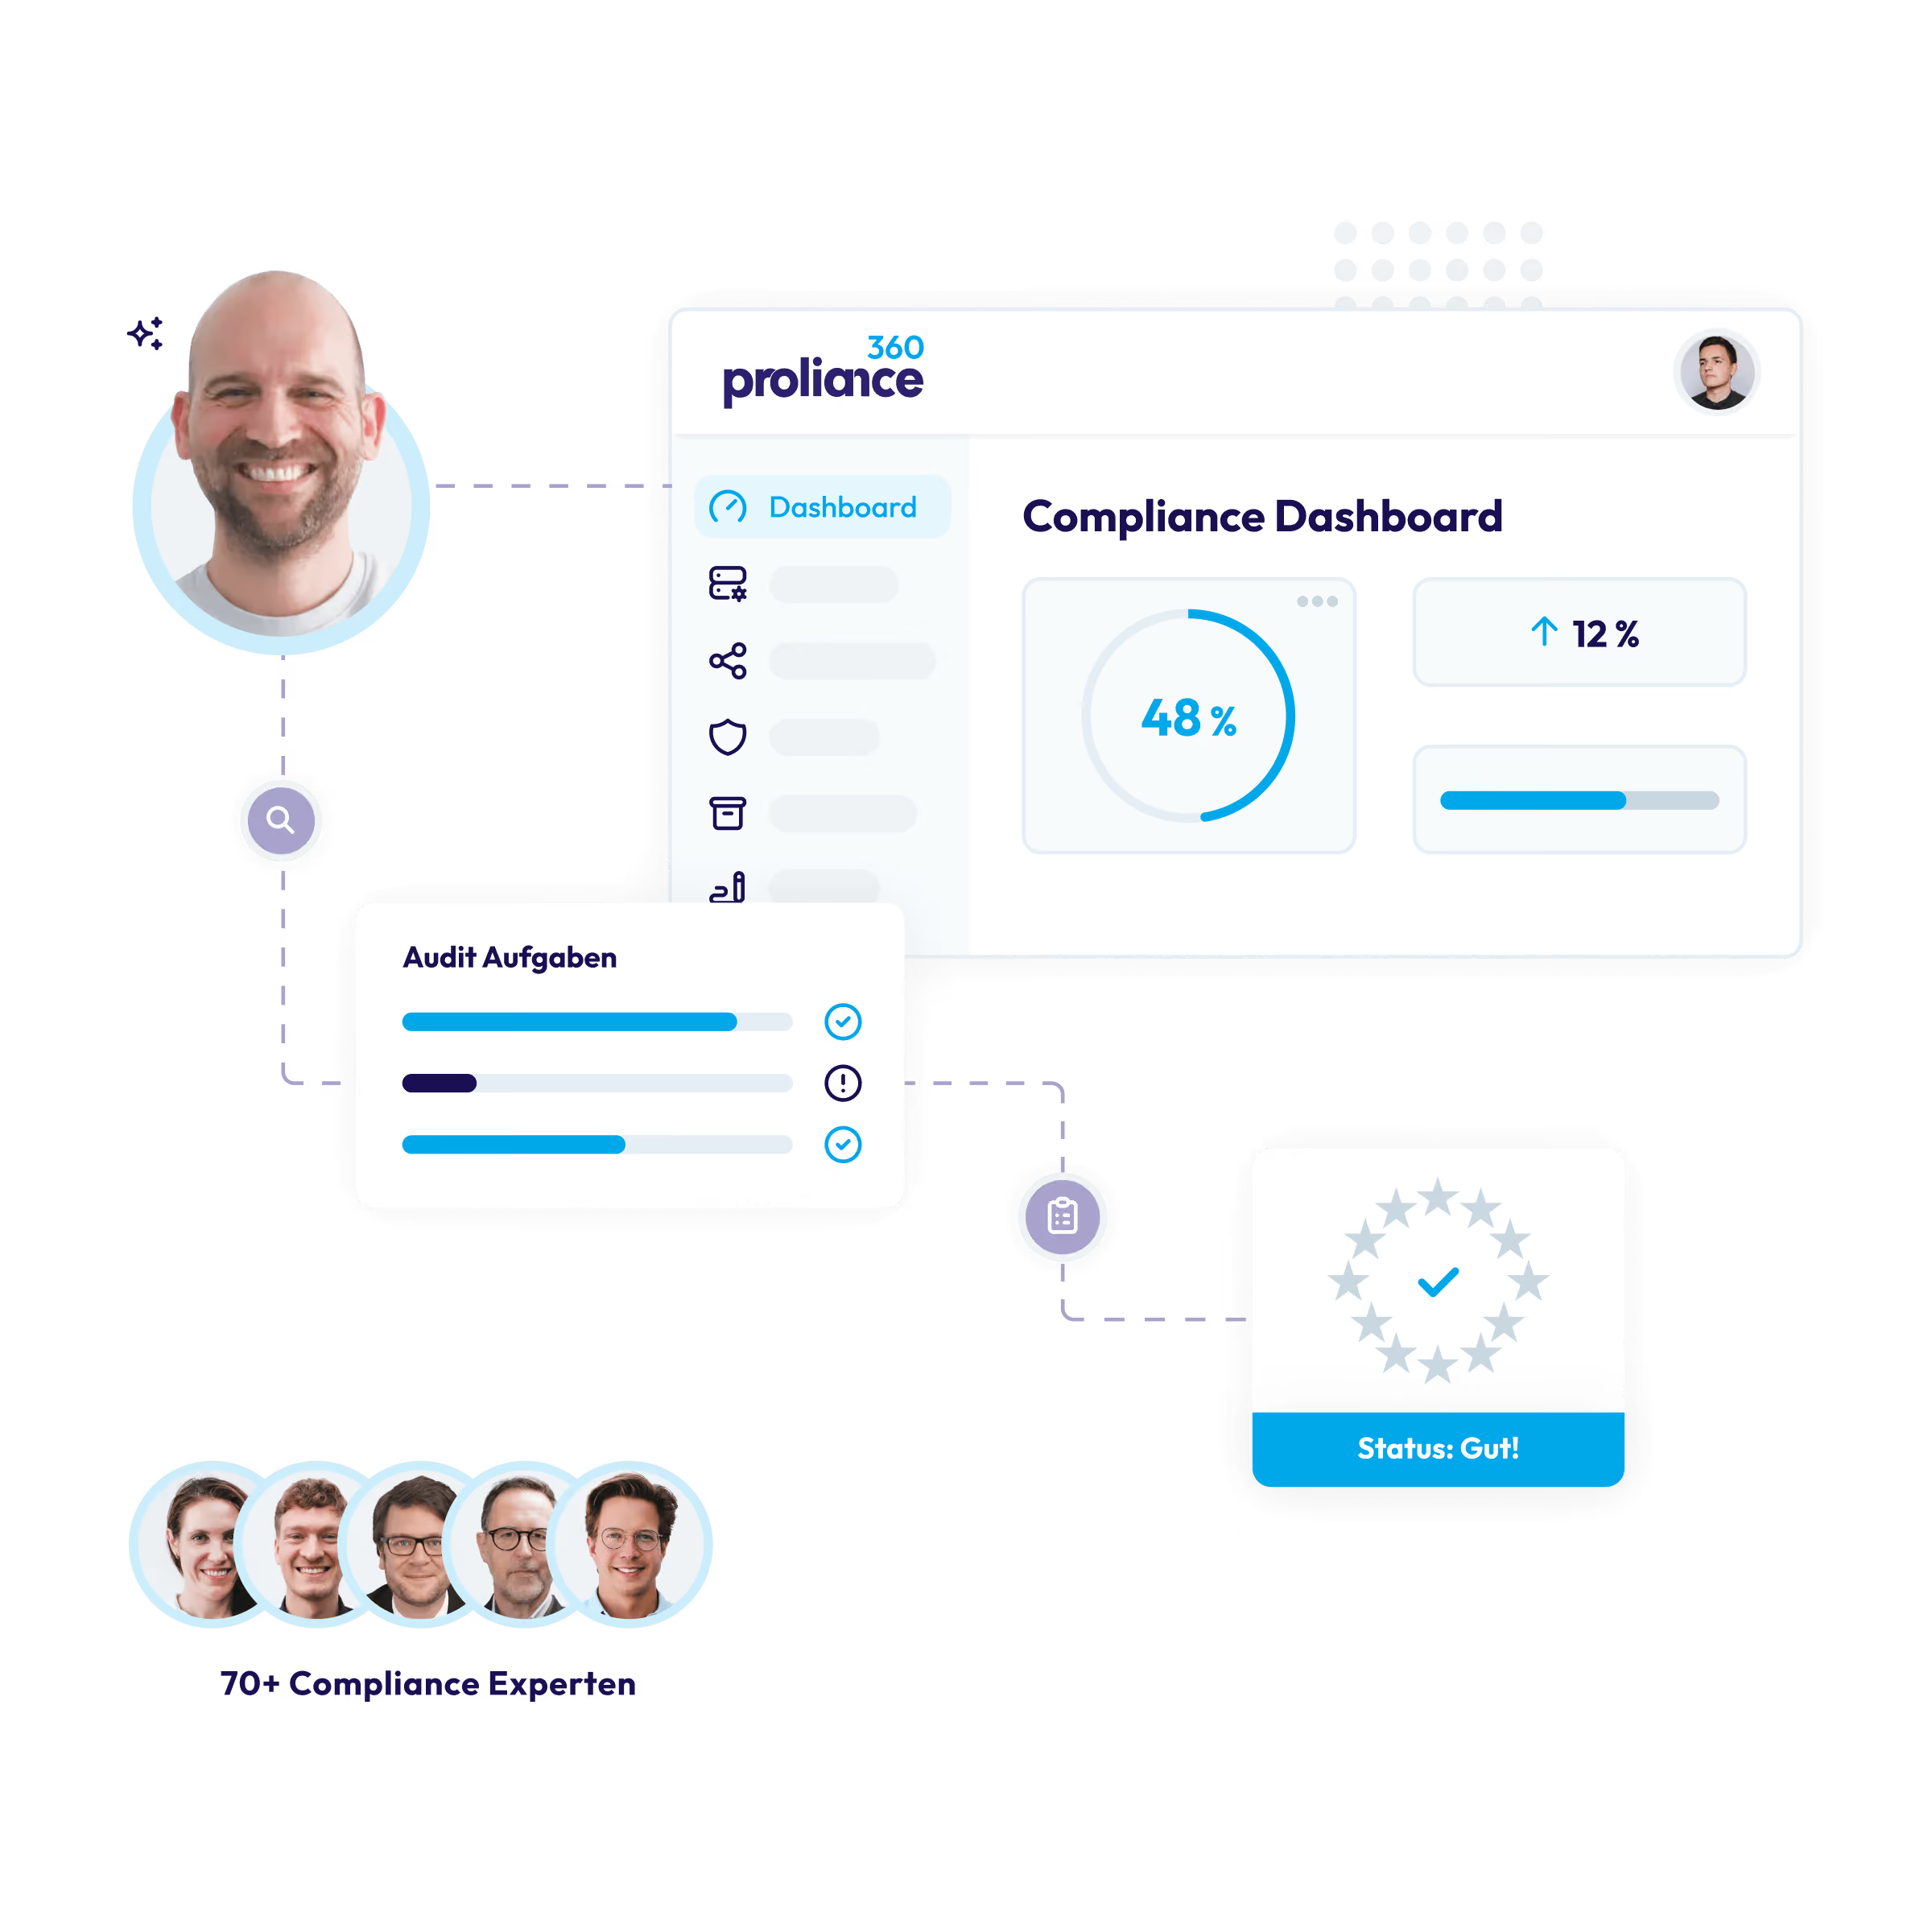
Energy suppliers and municipal utilities must now comply with multiple sets of regulations simultaneously: GDPR, NIS2, the IT Security Catalogue, the EU AI Act and the Whistleblower Protection Act. Proliance brings these topics together on one platform and provides you with experts who understand your industry.
This is how you achieve legal certainty and audit readiness without your team getting bogged down in Excel spreadsheets and email chains.




What data protection and IT risks do energy suppliers and municipal utilities face?
When customer data is leaked, systems fail, or clients demand proof of compliance, it quickly becomes a matter of time, money, and trust.

End-to-end compliance for the energy sector
Instead of coordinating three different service providers, Proliance gives you software and consultancy from a single team. Straightforward, integrated and practical for your day-to-day operations.

Data protection
Practical, everyday documentation.
- External Data Protection Officer
- Records of processing activities, data processing agreements and technical and organisational measures
- Data protection impact assessments and data breach management
Audit-ready documentation and a dedicated contact person for your queries.

Information security
Structured and prepared.
- ISMS implementation with Proliance InfoSec
- ISO 27001 gap analysis and preparation for ISO 27001 / TISAX®
- NIS2 implementation and management training
Security certification for your clients – without overwhelming your IT team.

AI Compliance
Working productively with AI.
- AI policy for your company
- Classification of your AI applications under the EU AI Act
- AI literacy training for employees
A clear framework for AI that protects project and client data.
Whistleblower protection
Proliance Whistle: reporting channel, documentation and case management, managed by experts. For companies with at least 50 employees that require an internal reporting office.

Training for your team
Short online training courses on data protection, information security, whistleblower protection and AI. Helping your team identify risks and take the right action in their day-to-day work.
Which energy suppliers and municipal utilities is Proliance suitable for?
For management, legal, IT, security and compliance teams – from municipal utilities to energy producers.
- Municipal utilities and local authority suppliers - (Limited compliance resources, multiple entities and high reporting obligations.)
- Network operators (electricity, gas, heat, water) - (High security requirements, critical infrastructure (KRITIS) regulations and regulatory evidence.)
- Energy producers and operators of renewable energy plants - (Technical systems, supply chains and new AI applications require clear rules.)
- Energy service providers, sales and metering point operations - (Customer data, third-party providers and fast-paced processes require clear responsibilities.)
- Groups and corporate networks with multiple entities - (Group-wide evidence, roles and responsibilities.)
Does this sound familiar?
- You are growing: around 20 people are now regularly working with personal data.
- A client is requesting proof of data protection or security compliance.
- Your current data protection officer is no longer responding.
- There has been a data breach or a phishing incident.
- Your team is using AI tools – but there are no guidelines in place yet.
How our compliance consultancy works for energy suppliers and municipal utilities


Data protection and IT security: 5 immediate steps for your planning office
You don't need to wait for an initial consultation. These measures will move your business forward immediately.

Clarify access rights
Who is authorised to access plans and client data? Enable multi-factor authentication.
Encrypt data
Encrypt laptops, smartphones and cloud storage containing sensitive data.
Record service providers
Create a list of all data-processing tools and service providers – the foundation for data processing agreements.
Establish an AI policy
To start with: "No client or project data in public AI tools."
Raise team awareness
Schedule a short training session on phishing and data protection.
Request a free consultation for construction companies and architectural firms
Compliance that matters to you and works in practice
We create bespoke service packages tailored to your company size, processes, and goals. Together, we implement data protection, information security, whistleblower protection, and AI governance in a way that is legally compliant, clear, and practical for your day-to-day operations.



Frequently asked questions about data protection audits
Typically, this includes the General Data Protection Regulation (GDPR), requirements for cyber and information security (NIS2, critical infrastructure regulations, industry-specific security standards), the EU AI Act, and the Whistleblower Protection Act. Which specific obligations apply depends on your company type, size, and activities. We will clarify this with you during an initial assessment.
The energy industry is a highly critical sector. Whether your company is directly affected depends on factors such as its size, specific field, and role in the supply chain. We will assess this together and determine the necessary steps to take.
For certain network and plant operators, an ISMS and corresponding certification are legally or regulatorily required. For others, ISO 27001 serves as a recognised framework for implementing NIS2 requirements in a structured manner and demonstrating security to customers and partners.
Generally speaking, yes, as soon as a company employs a certain number of people to process personal data or carries out high-risk processing activities. You can appoint an external Data Protection Officer through Proliance.
Yes, generally for organisations with 50 or more employees. The reporting office must operate confidentially, acknowledge receipt of reports, investigate them, and provide feedback. We provide the channel, the process, and the training.
Companies that deploy AI systems also have obligations, for example regarding the AI literacy of their employees and risk assessment. We provide support through stocktaking, AI policy development, and training.
You get the best of both worlds: a platform for documentation and automation, plus experts on hand to answer your questions. This saves time and ensures a consistent data foundation across all your compliance topics.
Knowledge on data protection, information security, and AI compliance: guides, templates & magazine
Magazine


Guides & Reports
Data Protection Templates
Compliance in your facility – simple, secure, and from a single source.